Data Security
- Data encryption at-rest
- Data encryption in-transit
- Privacy- by-design
- Access Management
EPOS Digital Solutions are built for data security and compliance.
EPOS is committed to applying the highest security and compliance standards when it comes to your data. Internal and external processes and third-party audits are all set up to make EPOS a secure and trusted partner.
EPOS protects your data at rest and in transit in your on-premise or cloud deployments. Enterprise-grade security with rigorous controls ensures safe and efficient management of your EPOS devices. Baseline requirements follow best practices within the development and hosting of the solutions we offer to our customers.
Data Security
- Data encryption at-rest
- Data encryption in-transit
- Privacy- by-design
- Access Management
Secure Software Development
- Logging and frequent monitoring
- Security-by-design
- Segregation of duties
- Third-party testing
Corporate Security
- Security trainings
- Vendor management
- SOC II policies
- Facilities security
EPOS is certified according to ISO/IEC 27001, the internationally recognized standard for information security management systems (ISMS). This certification confirms that EPOS has established, implemented, and continuously improves a structured and risk‑based approach to information security across the organization.
In addition, EPOS is GDPR compliant and uses the System and Organization Control (SOC) framework for yearly audits. These audits provide further assurance of top‑level security in data storage, as well as the effectiveness of internal security policies, operational processes, and employee onboarding and training.
The SOC II report is intended to give customers additional transparency into the controls EPOS has implemented to support secure operations and regulatory compliance.
EPOS is GDPR compliant and uses the System and Organization Control (SOC) Type I as a framework for yearly audits. These audits verify the top-level security in data storage as well as internal security policies, processes and employee onboarding and training.
The purpose of the SOC II report is to help you understand the controls established by EPOS to support operations and compliance.
Need more information regarding the SOC II report?
EPOS Manager retrieves the following customer data by default: Name, email address, telephone number, IP address, MAC address and machine name.
Other non-personal data collected is related to the usage of: software, products, call activity statistics, softphone and host information where products are located.
The IT administrator can chose to enable anonymization in EPOS Manager, meaning that no personal data is collected.
As a standalone software, EPOS Connect does not collect any kind of personal data from users.
End-users who are added to specific tenants (by the IT administrator in EPOS Manager), get the same data collected as mentioned question #1 unless the IT administrator has enabled annonymazation with or without AD.
EPOS Manager is a SaaS solution which uses Microsoft Azure cloud services and Microsoft Azure SQL/NoSQL databases. Microsoft operates all infrastructure, nonapplication software, and all typical SaaS services, such as backup and encryption of stored data.
Customer data is stored on a multitenant basis with customer data logically segregated.
Yes - but this is optional for the customer. Based on the settings managed by the data controller, it is possible to anonymize data. EPOS is not able to identify users when this setting is activated.
The data is encrypted both in transit and at rest. Https protocol is used for the encryption of data in transit and Azure TDE is used for encryption at rest. It is stored on Microsoft Azure and located in the Northern Europe data center.
Data is stored as long as the customer is using EPOS Manager. If the customer requests their data to be deleted, the customers/data subject should expext the retention period to be 1 month before receiving final confirmation of deletion.
Strict processes have been established for data breaches in order to comply with data audits, the rights of data subjects (according to privacy best practice) and the European General Data Protection Regulation.
The following ports are used:
The solution and data can be recovered unless both the backup data and live data are destroyed simultaneously in the Microsoft data center. Microsoft Azure offers geo-replication that would mitigate this theoretical risk.
EPOS Manager provides enhanced data privacy features:
Bandwidth usage per machine:
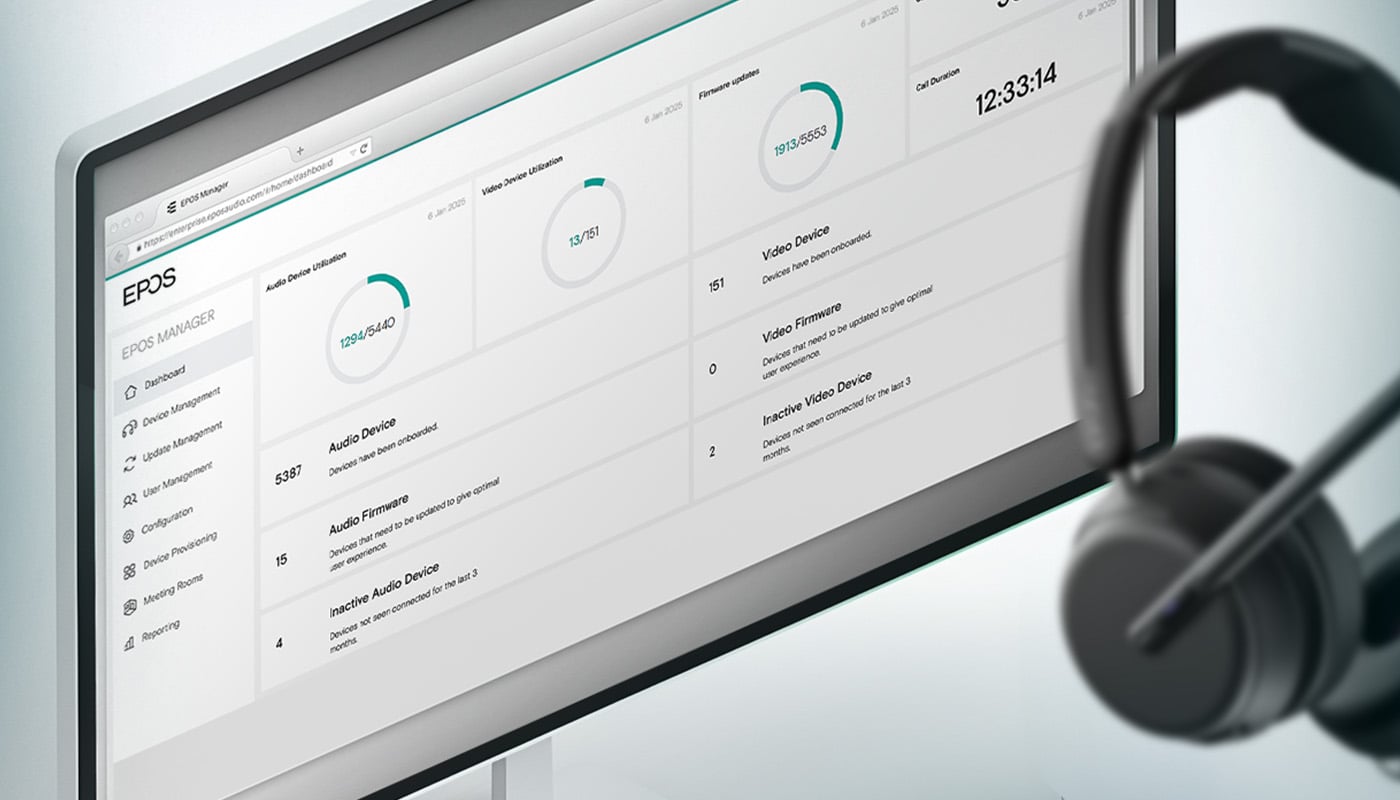
EPOS Manager
Save time and drive efficiency through remote update deployments and get insights into how to improve workplace productivity.
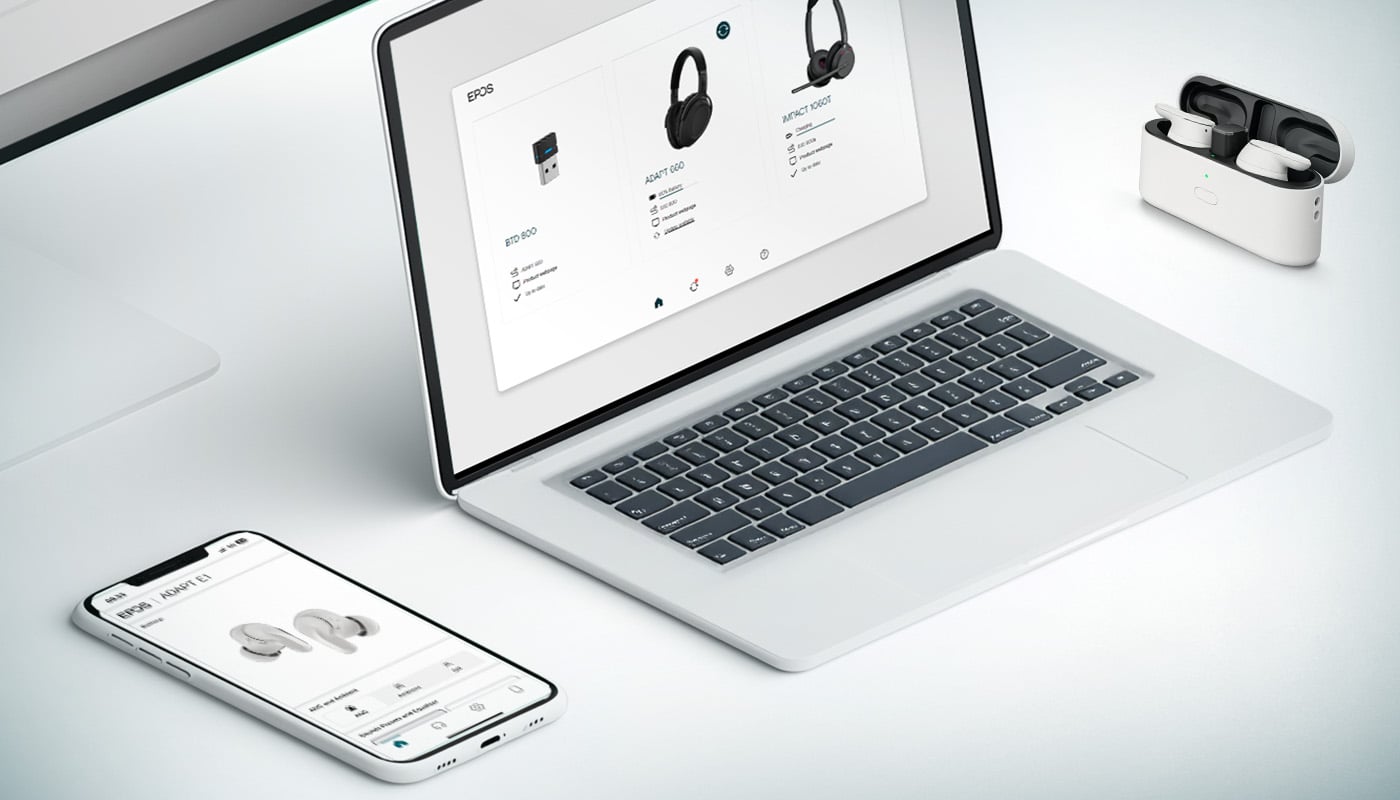
EPOS Connect
Update company devices with the latest firmware and personalize audio device settings to ensure flawless operation for end-users.
EPOS Developer portal
A simple, scalable, and secure platform for partners and customers to access all EPOS APIs and SDKs
Our products comply with mandatory EU directives through either an EU DOC (self-declaration) or an EU type examination certificate.
Learn more about EU directives
Building and maintaining trust with our customers, partners, and suppliers, are a top priority for EPOS. Our products aim to comply with relevant legislation that requires an appropriate reaction to software vulnerabilities.
EPOS vulnerability disclosure Policy follows the IoT Cybersecurity standard ETSI 303 645.
This policy includes:
Contact
Contact software support with your concerns about security and vulnerabilities with subject line: vulnerability_report
We handle every report of vulnerability with care.
What You Can Expect
When we receive a report of a possible vulnerability through the EPOS Security and Compliance Center, this is what the sender can expect regarding getting an answer:
Our Procedure
The triage of these reports will be done by our Vigilance Evaluation Board, using our internal Procedure called G-600 Vigilance.
The board has a system of vigilance that evaluate the vulnerabilities reports that come in.
They are scored on two parameters 1) Severity of thread & 2) Likelihood of the vulnerability being used.
For More Information
Please also contact us, if you want to hear more about the way we perform this triage, and how the Vigilance Board operates. This could be in the event of a Request for Proposals etc.